Hardening cameras: why default passwords and firmware updates keep being ignored
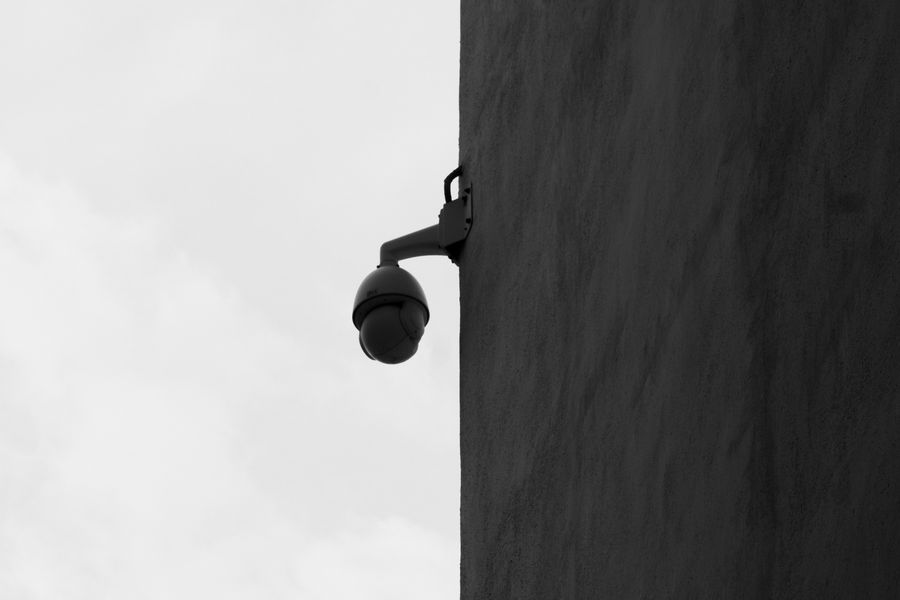
Reports of compromised surveillance devices are not rare, and post-mortems usually find that the attack was not sophisticated at all — a factory default password still in place, or firmware that had not been updated in years.
The exposure comes from three habitual practices. The first is connectivity at any cost: mapping a camera straight onto the public internet, so anyone who knows the address reaches a login page. The second is install and forget: default credentials never changed, and the device never entered a firmware update plan. The third is one password for everything: dozens of devices sharing a single credential, so one compromise opens the whole estate.
Hardening is not complicated, but it has to be built into the handover process: force a password change with complexity requirements during commissioning; close unnecessary service ports and reach devices through a platform or VPN rather than exposing them directly; audit firmware versions regularly and patch known vulnerabilities; enable alerts for anomalous logins and keep access logs in the operations record.
For manufacturers, requiring a password change at first login and providing a firmware update channel with a clear vulnerability response is moving from a nice-to-have to a baseline expectation.